VIMSVIMS

ISO 45001 in practice: implementation, required documents and preparing for the certification audit

ISO 45001 is the international standard that sets requirements for an occupational health and safety (OH&S) management system. It does not say how safe a given workstation must be — it describes how an organisation should systematically identify hazards, assess risk, involve workers, respond to incidents and keep improving. Certification is granted by an independent certification body after an audit, not by a consultancy or a software vendor.

An auditor is not looking for a thick binder. They are looking for evidence that what the procedures say actually happens on the shop floor — and that the organisation learns when something goes wrong.

  • ISO 45001
  • Certification audit
  • OH&S management system
  • Documentation

Published: 2026-10-01 · Updated: 2026-10-01 · 12 min · Varilo deployment team

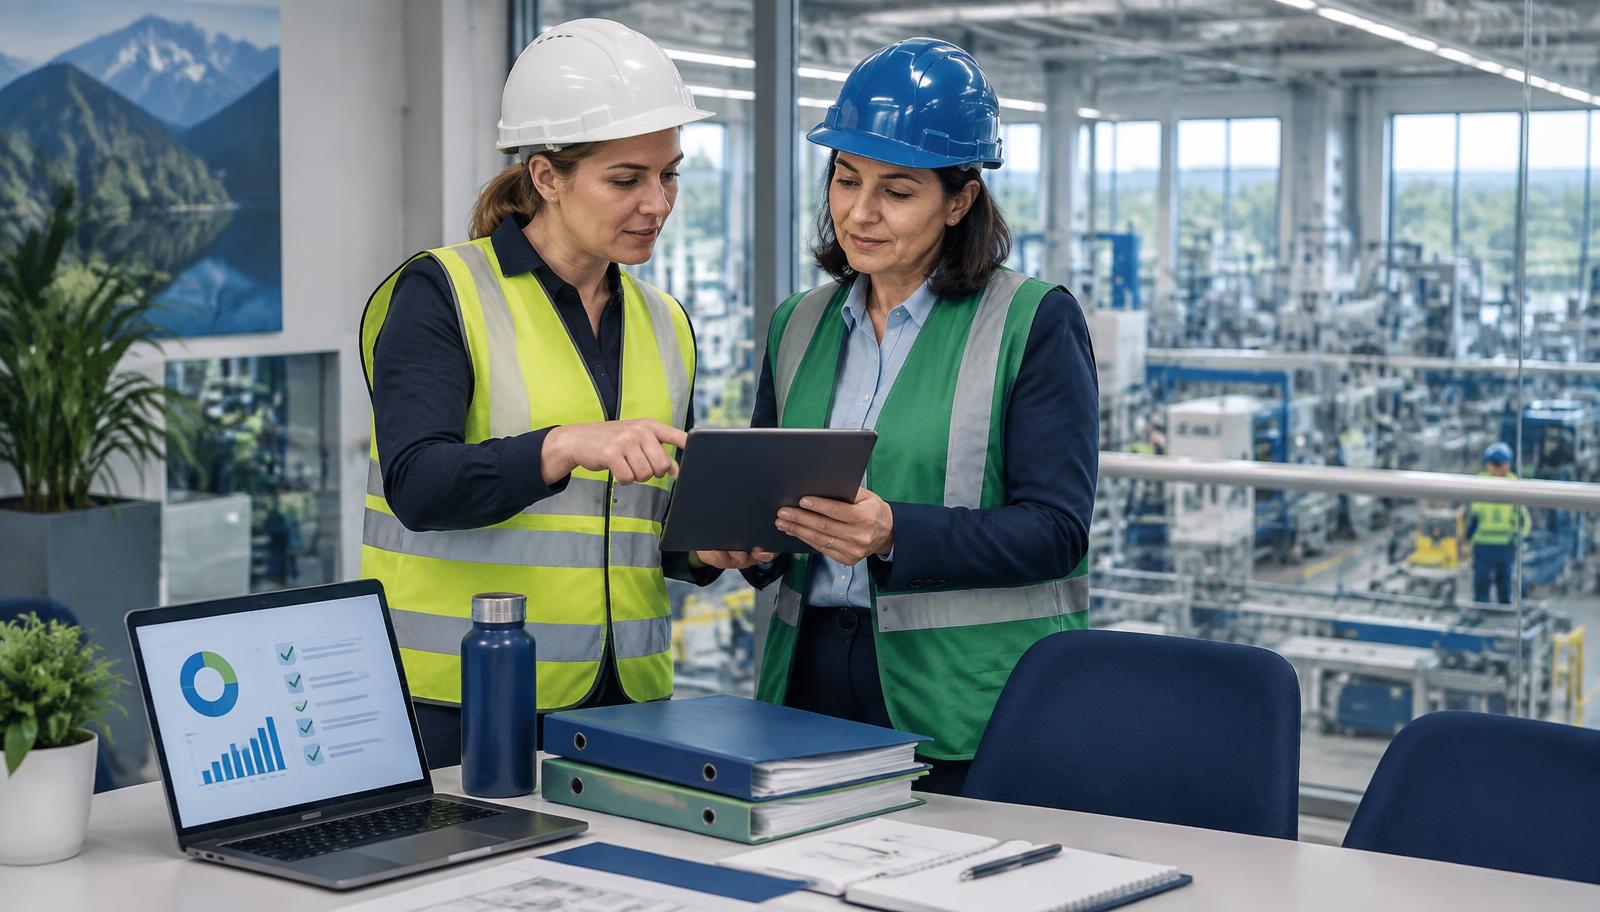
OH&S system lead and auditor reviewing ISO 45001 audit evidence on a tablet running V-IMS in a manufacturing plant

What ISO 45001 is and how it differs from legal compliance alone

ISO 45001 was published in 2018 and replaced the earlier OHSAS 18001 specification. It shares the high-level structure of ISO 9001 and ISO 14001, which makes it easy to combine with quality and environmental systems into one integrated management system.

Health and safety law sets the minimum an employer must meet. ISO 45001 is voluntary and concerns how safety is managed: who is accountable, how objectives are set, how performance is measured, how decisions are consulted with workers and how the organisation learns from incidents. Legal compliance is one of its requirements — the organisation must know its legal obligations and periodically evaluate whether it meets them.

The standard follows the PDCA cycle (plan — do — check — act). Requirements are set out in clauses 4–10: context of the organisation, leadership and worker participation, planning, support, operation, performance evaluation and improvement.

Who benefits from ISO 45001 certification

Most often certification is a customer requirement or a condition for tenders — especially in construction, automotive, energy and logistics. Insurers and corporate groups reporting ESG metrics increasingly ask for it too.

The internal effect matters just as much: clear responsibilities, one risk assessment method, corrective actions followed through and data management can act on. Organisations that treat the standard only as paperwork for customers usually struggle most during surveillance audits.

Which documents ISO 45001 requires

The standard no longer speaks of “procedures” and “records” but of “documented information”. Some must be maintained (documents describing how we work) and some retained (evidence that we did it). There is no requirement for a system manual or a procedure for every clause.

Required documented information includes: the scope of the OH&S management system; the OH&S policy; roles, responsibilities and authorities; the method and results of hazard identification and assessment of risks and opportunities; legal and other requirements; OH&S objectives and plans to achieve them; evidence of worker competence; emergency preparedness and response plans.

Evidence to be retained includes: monitoring and measurement results (including calibration where relevant); results of the evaluation of compliance; the internal audit programme and results; management review outputs; incidents and nonconformities with actions taken and their effectiveness; evidence of communication and worker consultation.

In most plants much of this data already exists — in risk assessments, accident registers, training and medical records and inspection reports. The challenge is not creating it but linking it into a consistent, current picture that is easy to show.

Implementation step by step

1. Gap analysis against the standard. 2. Context and scope: interested parties, their expectations and system boundaries. 3. Policy and responsibilities: top management commitment and how decisions are consulted with workers. 4. Risks and legal requirements: one risk assessment method, a register of legislation, objectives.

5. Operational controls: hierarchy of controls, management of change, contractor control, emergency preparedness. 6. Training and awareness. 7. Running the system and collecting evidence for several months. 8. Internal audit and management review. Only then is it worth approaching a certification body.

A typical implementation in a mid-sized organisation takes several months to over a year. The longest part is not writing documents but building habits: reporting incidents, closing actions on time and holding regular reviews.

The certification audit: stage 1 and stage 2

Certification takes place in two stages. Stage 1 assesses readiness: the auditor reviews documentation, scope, legal requirements, risk assessment results, the internal audit and management review. The output is a list of areas to address before stage 2.

Stage 2 is on site. The auditor interviews management and workers, walks the floor, checks whether the risk assessment reflects reality and picks random incidents to trace from report through root cause analysis to verification of action effectiveness. Workers are also asked whether they know how to report a hazard and whether they may remove themselves from dangerous situations.

Nonconformities are usually graded major or minor. A major one (for example no internal audit, or systematically unclosed corrective actions) can hold certification until it is resolved. A certificate is valid for three years, with annual surveillance audits.

Preparing for the audit — a checklist

Check that: the OH&S policy is current and known to workers; the risk assessment covers every role, including contractor and non-routine work; the legal register has a last-review date and compliance evaluation; objectives have measures and owners.

Also check that: every reported incident has a root cause analysis and an action with a deadline; overdue actions are explained; training and medical checks are current; a full internal audit cycle and a management review with documented decisions have taken place; process changes were risk-assessed before implementation.

Rehearse a short conversation with shift managers and supervisors: what the main hazards in their area are, how to report an incident and what changed after the last one. Auditors value these answers more than a presentation.

How V-IMS supports an ISO 45001 system

V-IMS does not issue certificates and does not replace a certification body or a competent person running the system. It organises the information auditors ask for most often in one place, with change history.

Hazard and incident reports go into a register from which you move to root cause analysis and CAPA actions with deadlines and owners. Risk assessment, training, competence and medical records, audits and inspections with checklists, work permits and management of change all work on shared data.

So before an audit there is no need to assemble evidence from many spreadsheets: the chain incident — cause — action — effectiveness check is visible in the system, and overdue items are visible before the auditor sees them.

Key takeaways

  • ISO 45001 is about how OH&S is managed, not only legal compliance; it follows PDCA and clauses 4–10.
  • The standard requires documented information but no system manual or procedure for every clause.
  • Certification has two stages — readiness review and on-site audit; certificates last three years with annual surveillance.
  • Common problems: outdated risk assessments, unclosed corrective actions and no evidence of worker consultation.
  • A system such as V-IMS makes evidence easier to collect and show, but only an independent certification body grants certification.

Frequently asked questions about ISO 45001

Is ISO 45001 mandatory?

No. It is voluntary. Health and safety law is mandatory; ISO 45001 certification is, however, often required by customers, tenders or corporate groups.

How long does ISO 45001 implementation take?

It depends on size and maturity. Usually several months to over a year, including the period of running the system needed to collect evidence before the audit.

How does ISO 45001 differ from OHSAS 18001?

ISO 45001 shares the structure of ISO 9001 and 14001 and places more emphasis on organisational context, top management and worker consultation and participation. OHSAS 18001 has been withdrawn.

Do I need special software for certification?

No. The standard requires no software. An EHS system does make it easier to keep data current, track deadlines and show evidence quickly during an audit.

Does V-IMS guarantee certification?

No. Certification decisions are made by an independent certification body based on the audit. V-IMS helps organise the processes and evidence assessed during it.

See how to organise your ISO 45001 audit evidence

In a demo we show how incidents, risk assessment, CAPA, training and audits connect in V-IMS into one consistent picture.